Cyberattack Triggers Mass Defrosting in EU Supermarkets
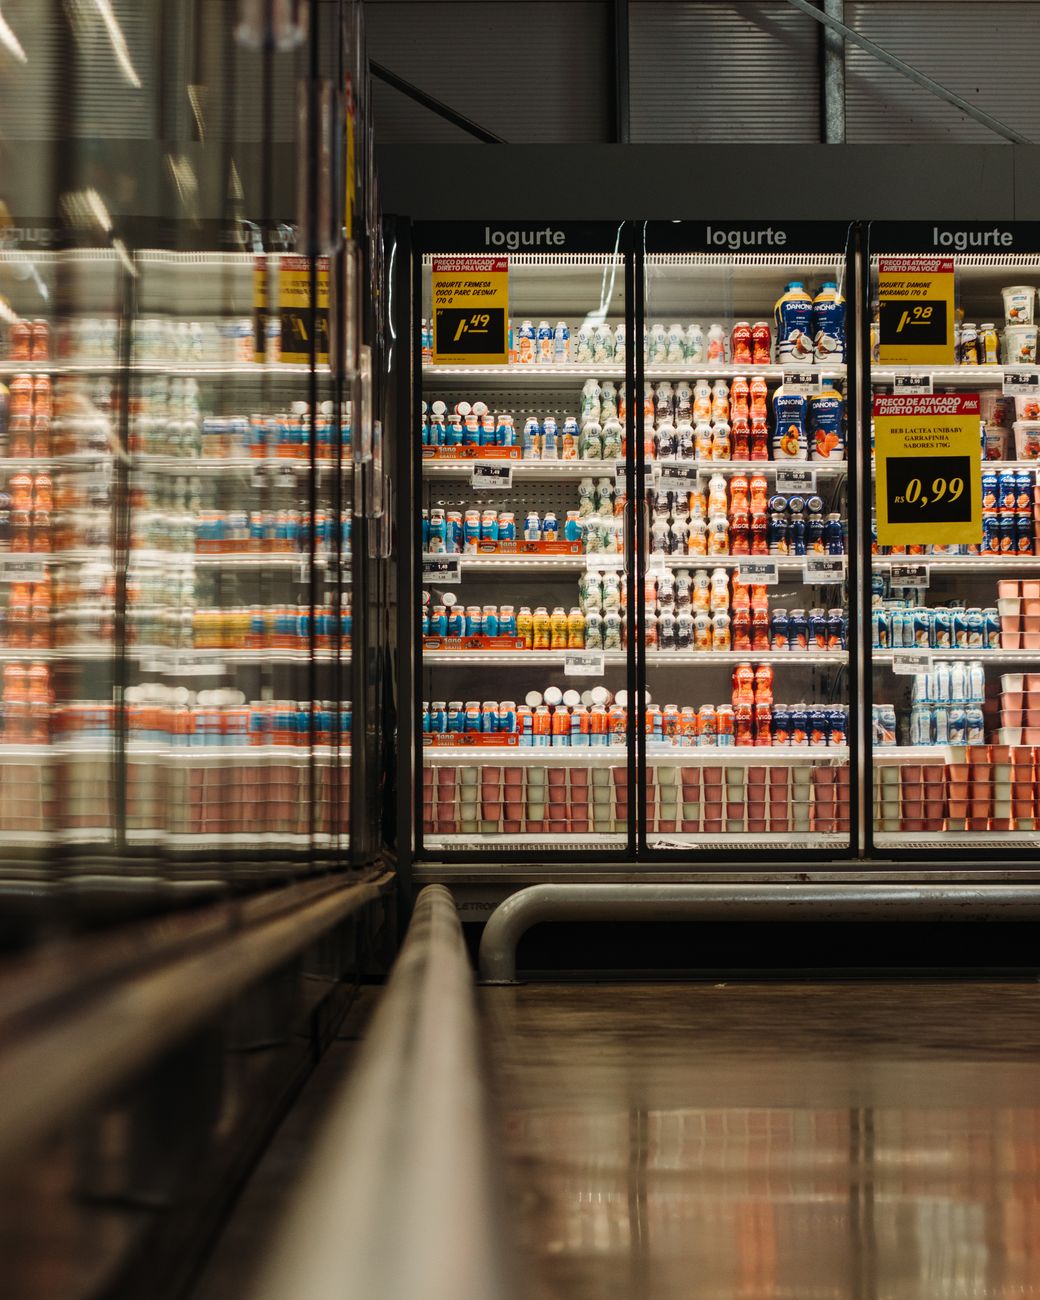
Key Takeaways
- •Hackers remotely activated automatic defrosting cycles in supermarket refrigeration units across Europe, causing significant operational disruption.
- •The attack likely exploited vulnerabilities in Industrial Control Systems (ICS) or Building Management Systems (BMS) managing retail cold chains.
- •Beyond immediate food spoilage, the incident highlights critical security gaps in interconnected IoT and OT infrastructure within retail.
- •This sophisticated attack could leverage compromised credentials, unpatched firmware, or exposed network interfaces to manipulate core refrigeration logic.
Technical Specifications & Data
| Control System Architecture | Distributed PLC/RTU network feeding into Central SCADA/BMS |
| Primary Communication Protocols | Modbus TCP/IP, BACnet/IP (often unencrypted at OT layer) |
| Estimated Affected Units (per store) | 10-50 refrigeration units (display cases, walk-ins, freezers) |
| Default Defrost Cycle Duration (typical) | 20-45 minutes per cycle (malicious activation can exceed) |
| Temperature Excursion During Attack | +5°C to +15°C above setpoint in frozen sections; +2°C to +8°C in chilled sections |
| Common Attack Vector Identified | Remote access vulnerabilities (e.g., unsecured VPN, default credentials, exposed RDP) |
| Estimated Food Spoilage Rate | 20-80% of temperature-sensitive inventory depending on duration and product type |
| System Access Method | Compromised administrator credentials or direct exploitation of network-exposed PLCs |
| Recommended Patching Cadence (OT) | Critical: Bi-monthly; Non-critical: Quarterly (often not met in practice) |
| Mitigation Strategy Highlight | Network segmentation, multi-factor authentication for remote access, robust anomaly detection |
| Industry Standard Compliance Gaps (observed) | IEC 62443 (Industrial Automation Security) and NIST CSF (Cybersecurity Framework) often not fully implemented in legacy retail OT |
Technical Architecture Overview: The Cold Chain's Digital Frontier
Modern supermarket refrigeration systems, far from being isolated units, are sophisticated networks of interconnected devices often managed by a centralized Industrial Control System (ICS) or a comprehensive Building Management System (BMS). These systems integrate various components: compressors, evaporators, condensers, temperature sensors, pressure transducers, and control valves. At their core are Programmable Logic Controllers (PLCs) or Remote Terminal Units (RTUs) that execute pre-programmed logic for refrigeration cycles, including the critical automatic defrosting function.
Communication within these systems typically relies on industrial protocols such as Modbus TCP/IP, BACnet/IP, or proprietary protocols. These protocols facilitate data exchange between sensors, actuators, and the central control unit, often connecting to a supervisory SCADA (Supervisory Control and Data Acquisition) system that provides operators with a graphical interface for monitoring and control. Remote access capabilities, essential for efficient maintenance and energy management, are usually facilitated through VPNs or secure gateways, allowing technicians or third-party service providers to interface with the system from off-site locations. The critical vulnerability often lies at these access points or within the network segmentation (or lack thereof) between the Operational Technology (OT) and Information Technology (IT) networks.
The automatic defrosting cycle itself is a carefully timed process, typically initiated based on frost accumulation detection (e.g., via pressure differential sensors or timed intervals) to maintain optimal heat exchange efficiency. Unauthorized activation of this cycle, as observed in the recent attacks, indicates a direct compromise of the PLC/RTU logic or the central SCADA system's command execution capabilities. This could involve manipulating specific registers within the PLC memory responsible for defrost initiation flags or overriding scheduled commands. The integrity of the network, the security of remote access credentials, and the robustness of firmware updates are paramount in preventing such malicious interventions.
"The complexity of integrated retail cold chain management presents a significant attack surface. A compromise here isn't just about data; it's about physical disruption and product integrity." - Cybersecurity Analyst specializing in OT.
Understanding these intertwined layers – from field devices to supervisory control – is crucial for comprehending how attackers can bypass traditional IT perimeter defenses to impact physical systems. The incident underscores the need for a holistic security approach that extends beyond standard IT practices into the unique domain of OT security.
Deep-Dive Systems & Performance Benchmarks: Exploiting Cold Chain Vulnerabilities
The precise mechanism for activating defrosting cycles likely involved exploiting common weaknesses found in many Industrial Control Systems (ICS) and IoT deployments. These vulnerabilities often include:
- Default or Weak Credentials: Many devices are installed with factory default passwords or easily guessed credentials, making them prime targets for brute-force attacks or dictionary attacks.
- Unpatched Firmware: OT devices often have extended lifecycles and may not receive regular firmware updates, leaving known vulnerabilities unaddressed for years.
- Insecure Remote Access: VPNs or remote desktop protocols (RDP) might be configured insecurely, lack multi-factor authentication, or be exposed directly to the internet without proper firewalls.
- Lack of Network Segmentation: A flat network architecture allows attackers, once inside the IT network, to easily pivot to the OT segment where refrigeration controls reside.
- Protocol Exploitation: Industrial protocols like Modbus or BACnet were not designed with security in mind and can be susceptible to command injection or manipulation if not properly secured at the application layer.
When an unauthorized defrost cycle is activated, the immediate operational impact is a significant spike in energy consumption as heating elements are engaged. More critically, the temperature inside the display cases and cold rooms rises, potentially exceeding safe thresholds for perishable goods. For example, fresh produce might tolerate a brief excursion to +8°C, but frozen goods require temperatures below -18°C. Prolonged or repeated defrost cycles can push these limits, leading to rapid degradation and spoilage. The typical defrost cycle duration can range from 20 to 45 minutes, but a malicious actor could force longer or more frequent cycles, preventing the system from reaching its set point and causing thermal stress on compressors and other components due to increased workload.
Performance benchmarks for secure cold chain operations include:
- Temperature Stability: Maintaining temperature within ±1°C of setpoint.
- Defrost Cycle Frequency: Optimized for minimal energy use and maximum efficiency, typically 4-6 times per 24 hours.
- Remote Access Security Posture: Implementation of strong authentication (e.g., 2FA/MFA), least privilege access, and strict firewall rules.
- Patch Management: Adherence to a rigorous schedule for critical firmware and software updates, even for legacy OT systems.
- Network Segmentation: A clearly defined perimeter between IT and OT networks, often with a DMZ (Demilitarized Zone) for secure gateway services, to contain potential breaches.
The attackers likely targeted the higher-level SCADA or BMS controllers that have a holistic view and control over multiple refrigeration units. Compromising these central points provides a 'master key' to disrupt operations across an entire facility or even multiple locations, as suggested by the pan-European nature of the incident. This type of attack is a stark reminder that physical outcomes can be directly manipulated by digital vulnerabilities.
Why This Matters & Industry Impact: Beyond Spoilage, a Call for OT Security
The incident of hackers forcing supermarket fridges into defrost mode carries far-reaching implications that extend beyond the immediate financial losses from spoiled food. It represents a significant escalation in the targeting of Operational Technology (OT) within critical retail infrastructure, highlighting vulnerabilities that could impact public health, economic stability, and national security.
Firstly, the Food Safety and Public Health impact is paramount. Unauthorized temperature excursions in refrigeration systems create ideal conditions for bacterial growth, rendering perishable goods unsafe for consumption. This necessitates massive product recalls, which are costly and severely damage consumer trust. The ability of hackers to manipulate environmental controls directly translates into a threat to the food supply chain itself, creating a novel form of cyber-terrorism against civilian infrastructure.
Secondly, the Economic and Reputational Damage for affected supermarket chains is immense. Beyond the cost of ruined inventory, there are expenses related to forensic investigations, system remediation, security upgrades, and potential regulatory fines. The reputational hit from being perceived as unable to protect core operations or consumer safety can have long-term effects on market share and brand loyalty. The incident also creates a ripple effect across the supply chain, impacting suppliers and logistics.
"This attack is a wake-up call for all industries relying on interconnected OT systems. The line between cyber and physical threats is blurring rapidly." - European Retail Federation Spokesperson.
Thirdly, this event serves as a critical Cybersecurity Wake-Up Call for the entire retail and critical infrastructure sector. It demonstrates that attackers are moving beyond data exfiltration and ransomware to directly manipulate physical processes. The incident underscores the urgent need for:
- Robust OT Security Frameworks: Implementing specific security protocols, tools, and expertise tailored for OT environments, distinct from traditional IT security.
- Enhanced Network Segmentation: Strictly isolating OT networks from IT networks to prevent lateral movement during a breach.
- Supply Chain Security Audits: Ensuring that third-party vendors and contractors who have remote access adhere to stringent security standards.
- Incident Response Planning for OT: Developing and regularly testing specific response plans for cyber-physical attacks that consider the unique challenges of OT systems.
- Employee Training and Awareness: Educating staff about phishing, social engineering, and the importance of secure practices.
The incident should prompt a comprehensive re-evaluation of security postures across all industries that rely on interconnected control systems, from manufacturing and energy to transportation and healthcare. It emphasizes that physical world resilience is increasingly dependent on digital security, making investment in proactive OT security measures an unavoidable imperative for business continuity and societal well-being.
Strengthen your organization's cyber resilience with leading OT security solutions and services. Consult with our experts today!
Chronological Timeline
Initial reports from isolated supermarket branches in France and Germany noting anomalous defrost cycles and temperature warnings.
Multiple supermarket chains across various European countries confirm coordinated cyberattacks targeting their refrigeration control systems.
Forensic investigations begin, identifying common attack vectors involving compromised remote access points and ICS vulnerabilities. Industry alerts issued.
Supermarket chains implement emergency security measures, including isolating OT networks and enforcing mandatory password resets for all remote access accounts.
Long-term remediation efforts underway, focusing on comprehensive OT security audits, network segmentation, and enhanced threat monitoring across European retail.
Frequently Asked Questions
What specifically allowed hackers to activate defrosting cycles?
What are the primary risks of unauthorized defrosting?
How can supermarkets protect their refrigeration systems from similar attacks?
Daily Specs Editorial Staff
Lead Technical Analyst & Hardware Researcher
The Daily Specs editorial staff compiles, benchmarks, and verifies emerging technical specifications directly from system architecture manuals, hardware datasheets, and open-source codebases to deliver high-gain technical intelligence.